Key Takeaways
- Railway paused builds and deploys on every plan and in every region on October 21, and they were still paused at 03:00 UTC on October 22.
- Railway says an outsider may have read encrypted environment variables and, for some, the decrypted values.
- Change each key at its provider now. A key that leaked works against that provider directly, with or without Railway.
Railway had a very bad day. Its dashboard, API and command line tool went down early on October 21, and builds stopped in every region. Then, at 21:59 UTC, it posted a security notice. It says an outsider may have read the secrets its customers store there.
Background: the checks every business site needs.
If you run anything on Railway, do not wait for builds to come back. Start changing keys at the source tonight.
What Railway Says Happened
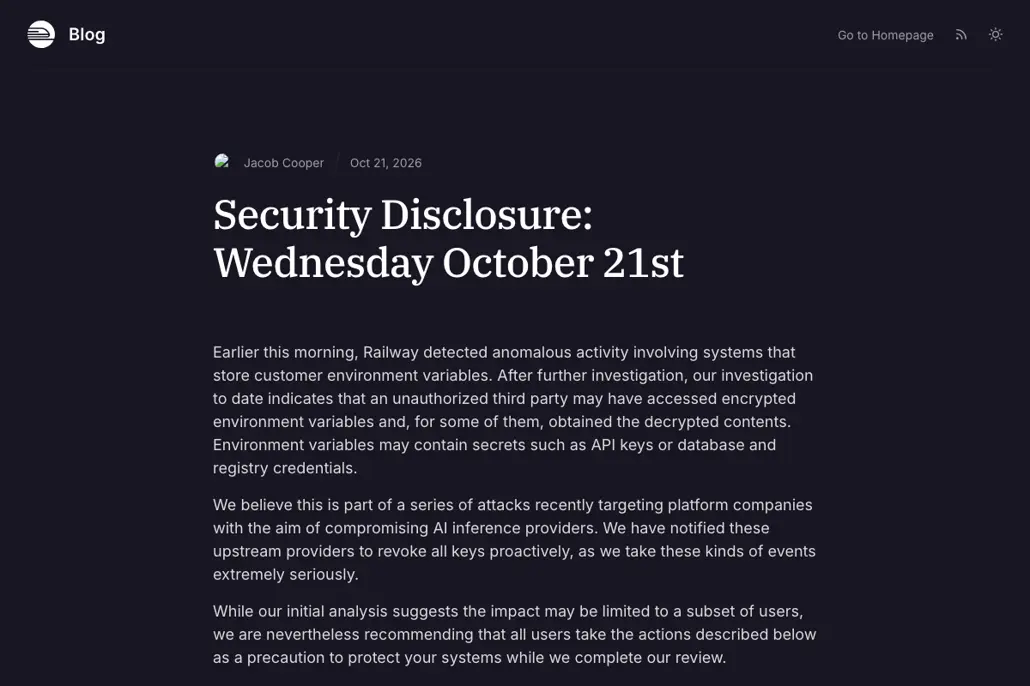
Railway's security disclosure says it found unusual activity in the systems that hold customer environment variables. Those are the settings where apps keep API keys, database passwords and registry logins.
- An outsider may have read encrypted variables.
- For some of them, the outsider may also have the decrypted values.
- Railway thinks this is part of a series of attacks on platform companies, aimed at getting into AI providers.
- It has asked those providers to revoke keys on their side.
- Its first look says only some users were hit. It still tells every user to act.
- It will email the accounts it confirms were affected.
Railway has not said how many accounts that is, when the access began or who did it.
The Day in Order
Railway's status page logged about two dozen updates in under 20 hours. These are the ones that change what you can do.
| Time (UTC) | What Railway posted |
|---|---|
| Oct 21, 07:24 | Looking into a problem |
| Oct 21, 09:28 | Dashboard, API and CLI down. Builds paused in all regions. Support down too. |
| Oct 21, 11:33 | API back, some features still off, builds still paused |
| Oct 21, 19:15 | Builds to return in stages. Enterprise, then Pro, then Hobby, then Free and Trial. |
| Oct 21, 20:19 | OAuth sessions wiped, so everyone has to log in again |
| Oct 21, 21:59 | Security notice. Revoke every variable stored in Railway and check your logs. |
| Oct 21, 22:10 | Railway starts resetting every bucket key itself |
| Oct 22, 01:22 | Guides posted for the next steps |
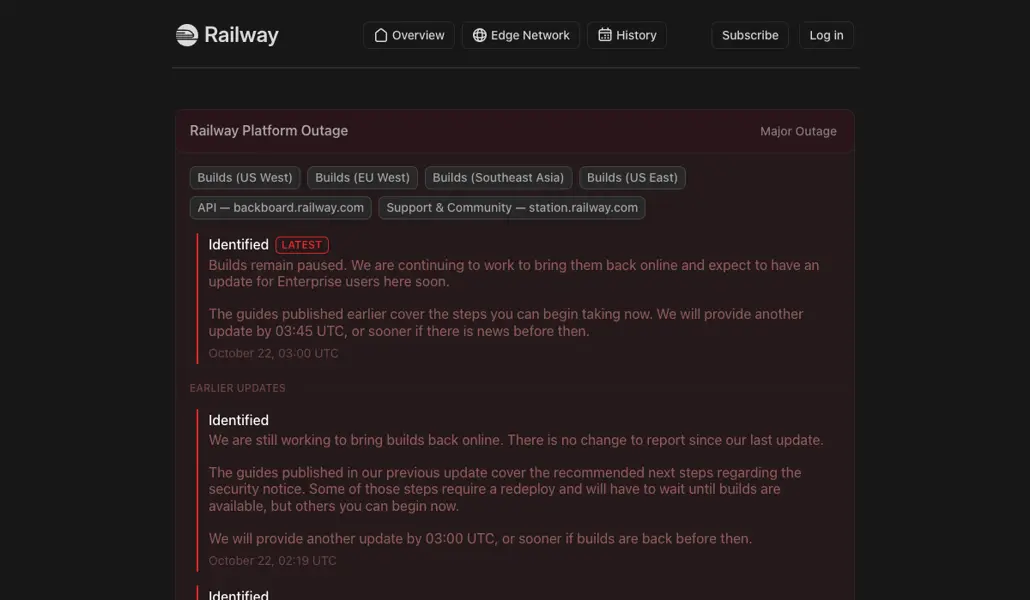
| Oct 22, 03:00 | Builds still paused. Next update due by 03:45. |
Pacific time is seven hours behind UTC, so the security notice landed at 2:59 p.m. on the West Coast.
The Issues Still Open
This is where it gets messy. These are the problems people are stuck with tonight.
- You cannot deploy. Builds are off on every plan. A bug fix, a new feature or a new key cannot ship until they come back.
- New keys cannot reach a running app. Apps read their settings when they start. Change a key in Railway and the live service keeps the old one until a redeploy, which you cannot do yet.
- Bucket keys were changed under you. Railway reset the access keys for every storage bucket. A service still holding the old ones may fail to read or write files until it redeploys.
- GitHub links were cut. Railway says it cut the tokens behind your GitHub connection. You will have to reconnect it, and autodeploy may be off.
- Old registry tokens still work. Railway removed GitHub tokens saved as registry logins, but they keep working on GitHub until you revoke them there.
- Support was down too. The support and community site, station.railway.com, was listed as affected most of the day.
- Everyone got logged out. Railway wiped login sessions at 20:19 UTC.
- Scope is still unknown. No account count, no start time and no attacker named yet.
What to Rotate First
Railway's own advice is to roll every variable, every API key and every private registry login. It is a lot. Go in this order, the ones that cost money or open data first.
- Payment keys. Stripe and any other card processor. Railway posted a guide just for Stripe.
- AI provider keys. OpenAI, Anthropic, OpenRouter and Grok. Railway says AI providers were the real target. Check usage for spend you did not make.
- Database passwords. Postgres, MySQL, MongoDB and Redis. Railway has a guide for each.
- Cloud accounts. AWS and Google Cloud keys. Look for new users, new keys or servers you did not start.
- GitHub. Revoke old tokens and check for deploy keys or webhooks you do not know.
- Email, text and everything else. Any service that can send as your business or bill you.
Change each key at the provider first. Then save the new value in Railway so the next deploy picks it up. When builds come back, redeploy, then turn off the old key. Some providers, Authorize.net for one, let the old key live a while so you can switch without downtime.
Why You Cannot Just Wait
A stolen key does not need Railway to work. Someone with your OpenAI key can spend on your OpenAI account. Someone with your database password can reach your database if it is open to the internet. Railway being down does not slow them down.
So the fix happens at each provider, not inside Railway. That part you can do tonight, builds or no builds.
Railway's Guides
Railway posted 13 short guides by 02:19 UTC on October 22. They cover usage checks for OpenRouter, Grok, Anthropic, OpenAI and Stripe. They also cover password changes for Postgres, MongoDB, Redis and MySQL, access checks for GitHub, AWS and Google Cloud, and how to redeploy buckets and reconnect GitHub. All of them link from the status page.
We will update this story when builds come back or Railway says how many accounts were hit.
Before You Call
Is Railway down right now?
As of 03:00 UTC on October 22, 2026, Railway's status page still showed a major outage. The API came back that morning, but builds and deploys were paused in all four build regions. Check status.railway.com for the latest.
What happened in the Railway security incident?
Railway says it saw unusual activity in the systems that store customer environment variables on October 21, 2026. It believes an outsider may have read encrypted variables and, for some of them, the decrypted contents. Railway ties it to a wave of attacks on platform companies aimed at AI providers.
Do I need to rotate my Railway environment variables?
Yes. Railway tells every user to roll all environment variables, API keys and private registry credentials, even though it says only a subset of users may be affected. It will email accounts it confirms were hit.
Can I redeploy on Railway with new keys?
Not yet, as of 03:00 UTC on October 22. Builds are paused, so a running service keeps its old values until builds come back. You can still change keys at each provider now and put the new values in Railway, ready for the next deploy.
Why did Railway log me out?
Railway invalidated OAuth sessions at 20:19 UTC on October 21 as part of the fix. Anyone signed in had to log in again.
Terms in This Story
Cited Pages
- Security Disclosure, Wednesday October 21st, Railway Blogblog.railway.com
- Railway Platform Outage, Railway Statusstatus.railway.com
- Redeploy Buckets and Reconnect GitHub After the Credential Reset, Railway Blogblog.railway.com
- Railway pauses deployments after possible exposure of customer environment variables, RuntimeWireruntimewire.com
Spot an error? Tell us through our contact form. We fix mistakes in the open, as our corrections policy explains.
Elsewhere on the Site
WordPress 7.1.2 Fixes a Critical Flaw Attackers Are Already Using
A core WordPress bug let attackers load PHP files without logging in. Attacks began within hours of the fix, and CISA now lists it as exploited.